Cyber Security Club
University of South Asia
Offensive thinking.
Defensive purpose.
Curiosity, research
& a different perspective.
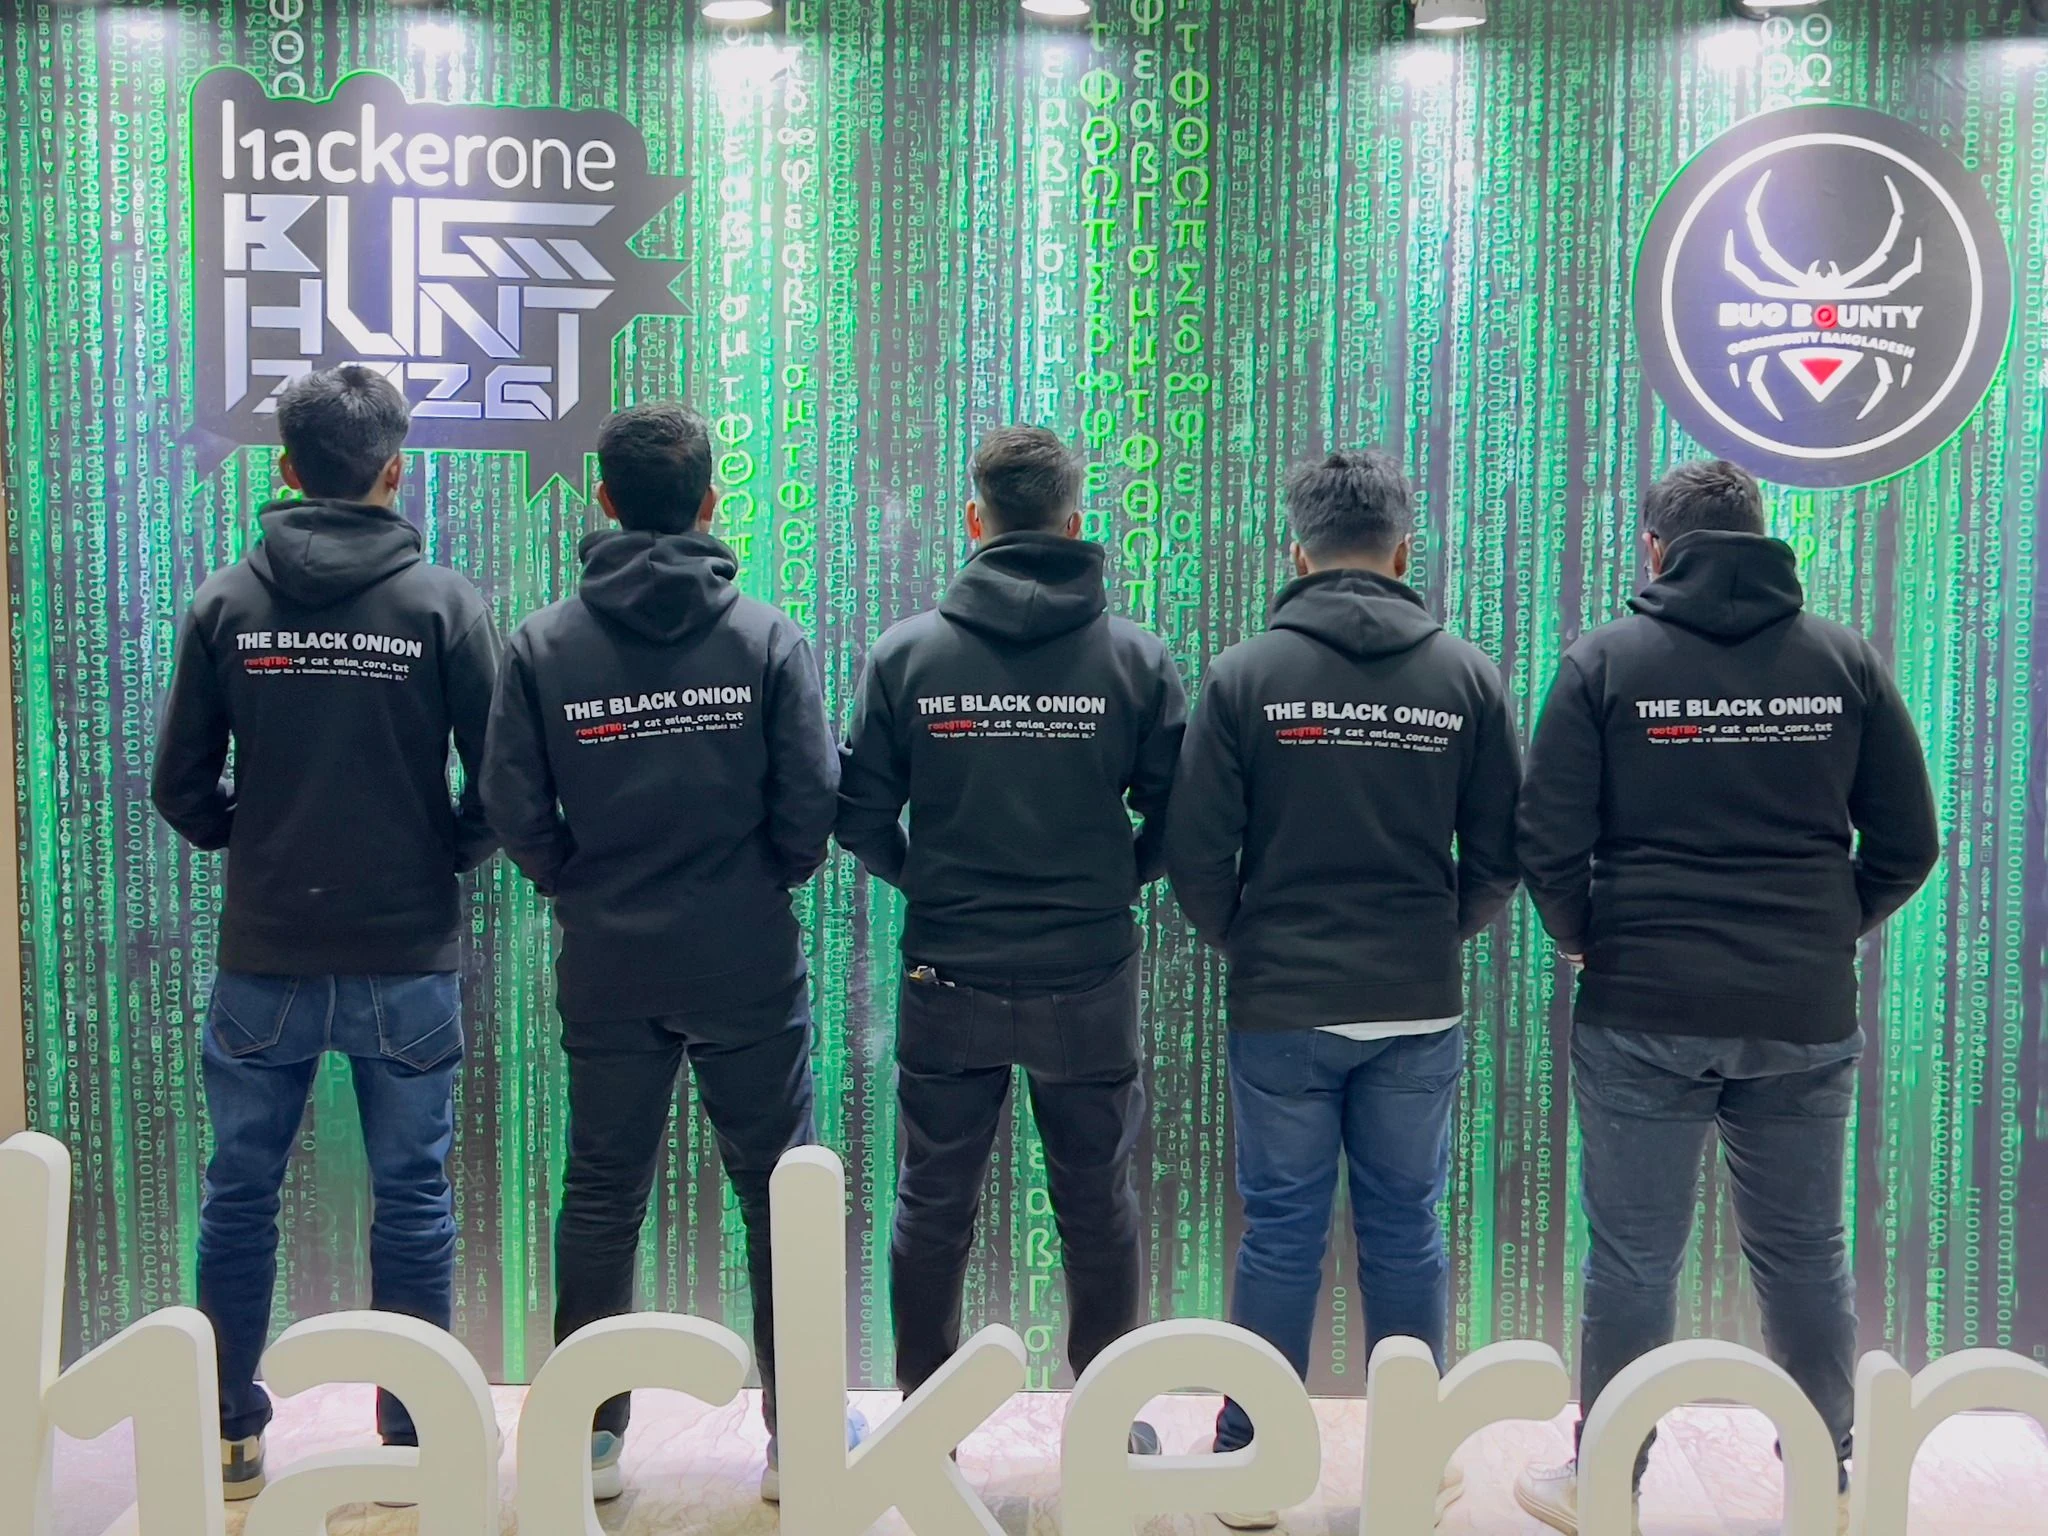
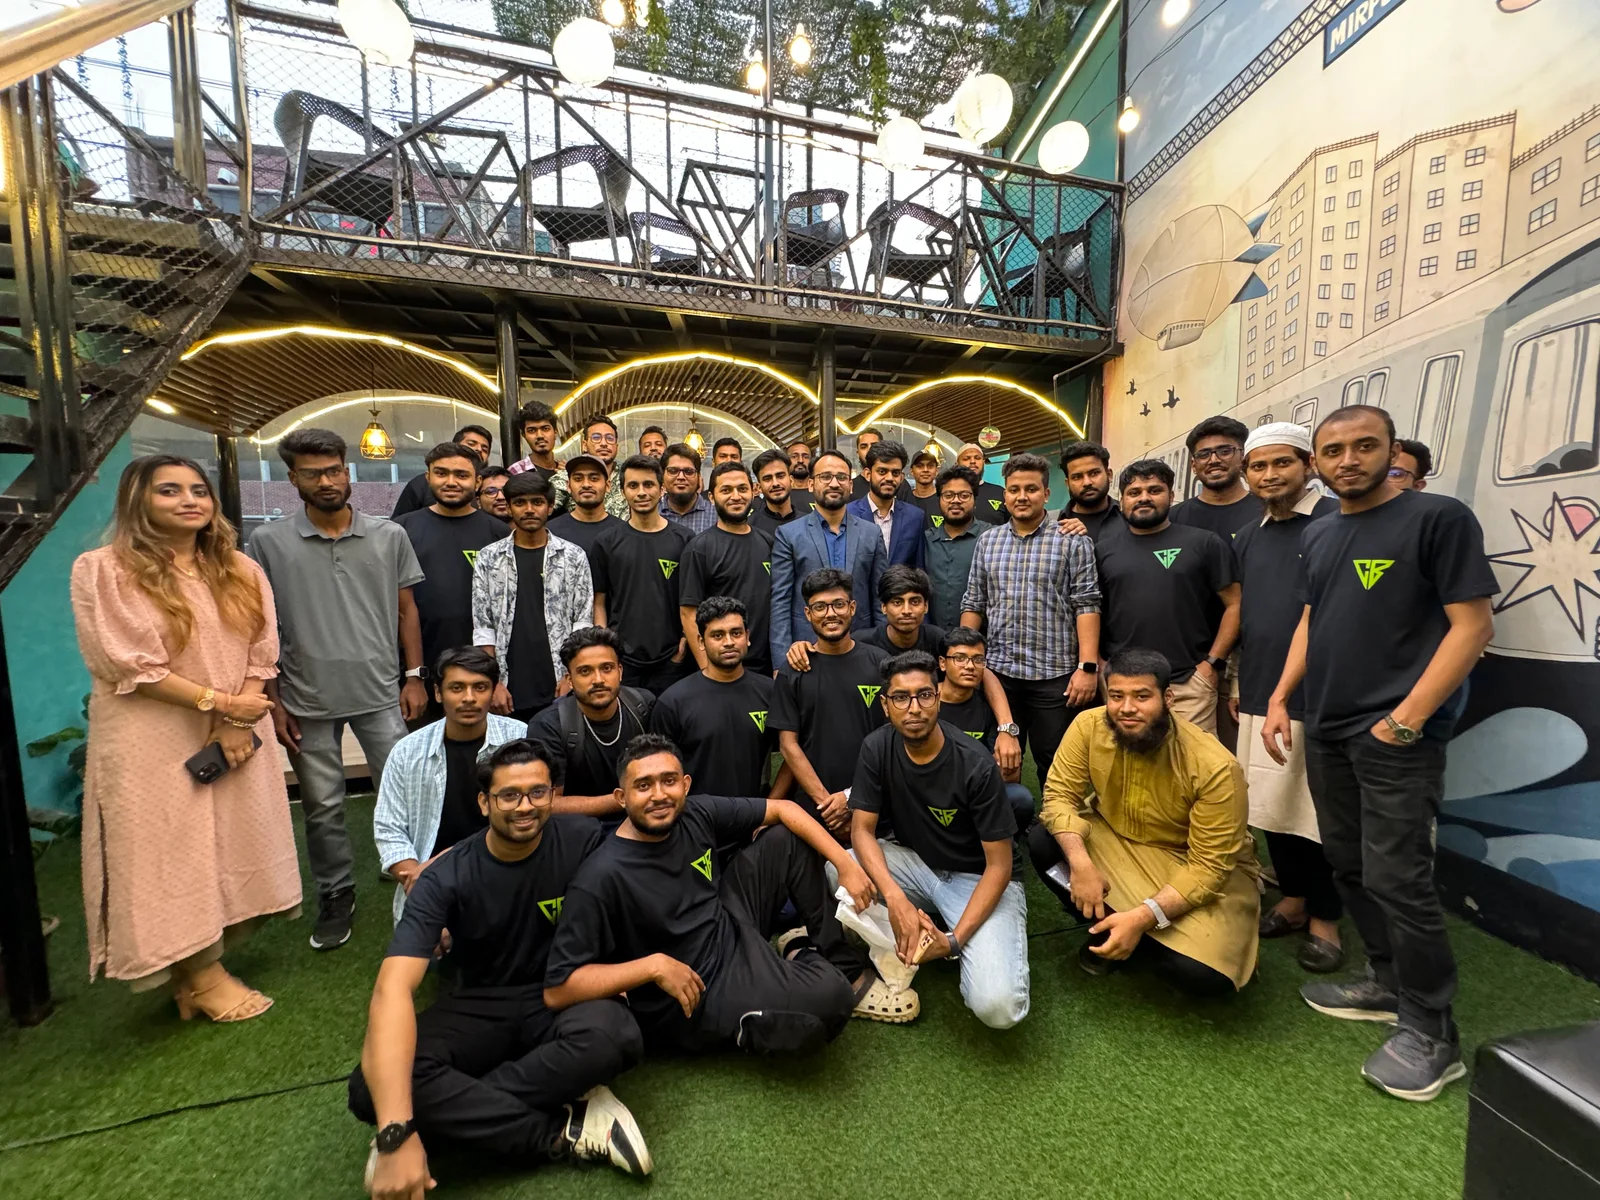
The people behind the work
A Bangladesh-based cybersecurity team. We test, research, and build security skills together.
Research-led security. Human ingenuity.
Meet Black OnionOur expertise
From your first assessment to the questions nobody has asked yet. Six ways we help teams understand their exposure and build stronger defenses.
Find the weaknesses that automated scans leave behind.
A focused assessment of your web applications, APIs, and network infrastructure. We investigate how vulnerabilities connect, explain their business impact, and help your team prioritize remediation.
Explore this serviceTest your defenses against an adversary-minded approach.
An objective-led security engagement built around your organization. We work within explicitly authorized boundaries to help you understand exposure and evaluate detection and response.
Explore this serviceGo deeper into the systems your business depends on.
Focused research into application behavior, binaries, and security controls. Our interests span reverse engineering, cryptography, exploit development, and responsible vulnerability research.
Explore this serviceUnderstand what your external footprint reveals.
Research into publicly accessible information to surface organizational exposure and add context to potential threats. Collection boundaries and intended use are agreed before work begins.
Explore this serviceBuild security skills that stay with your team.
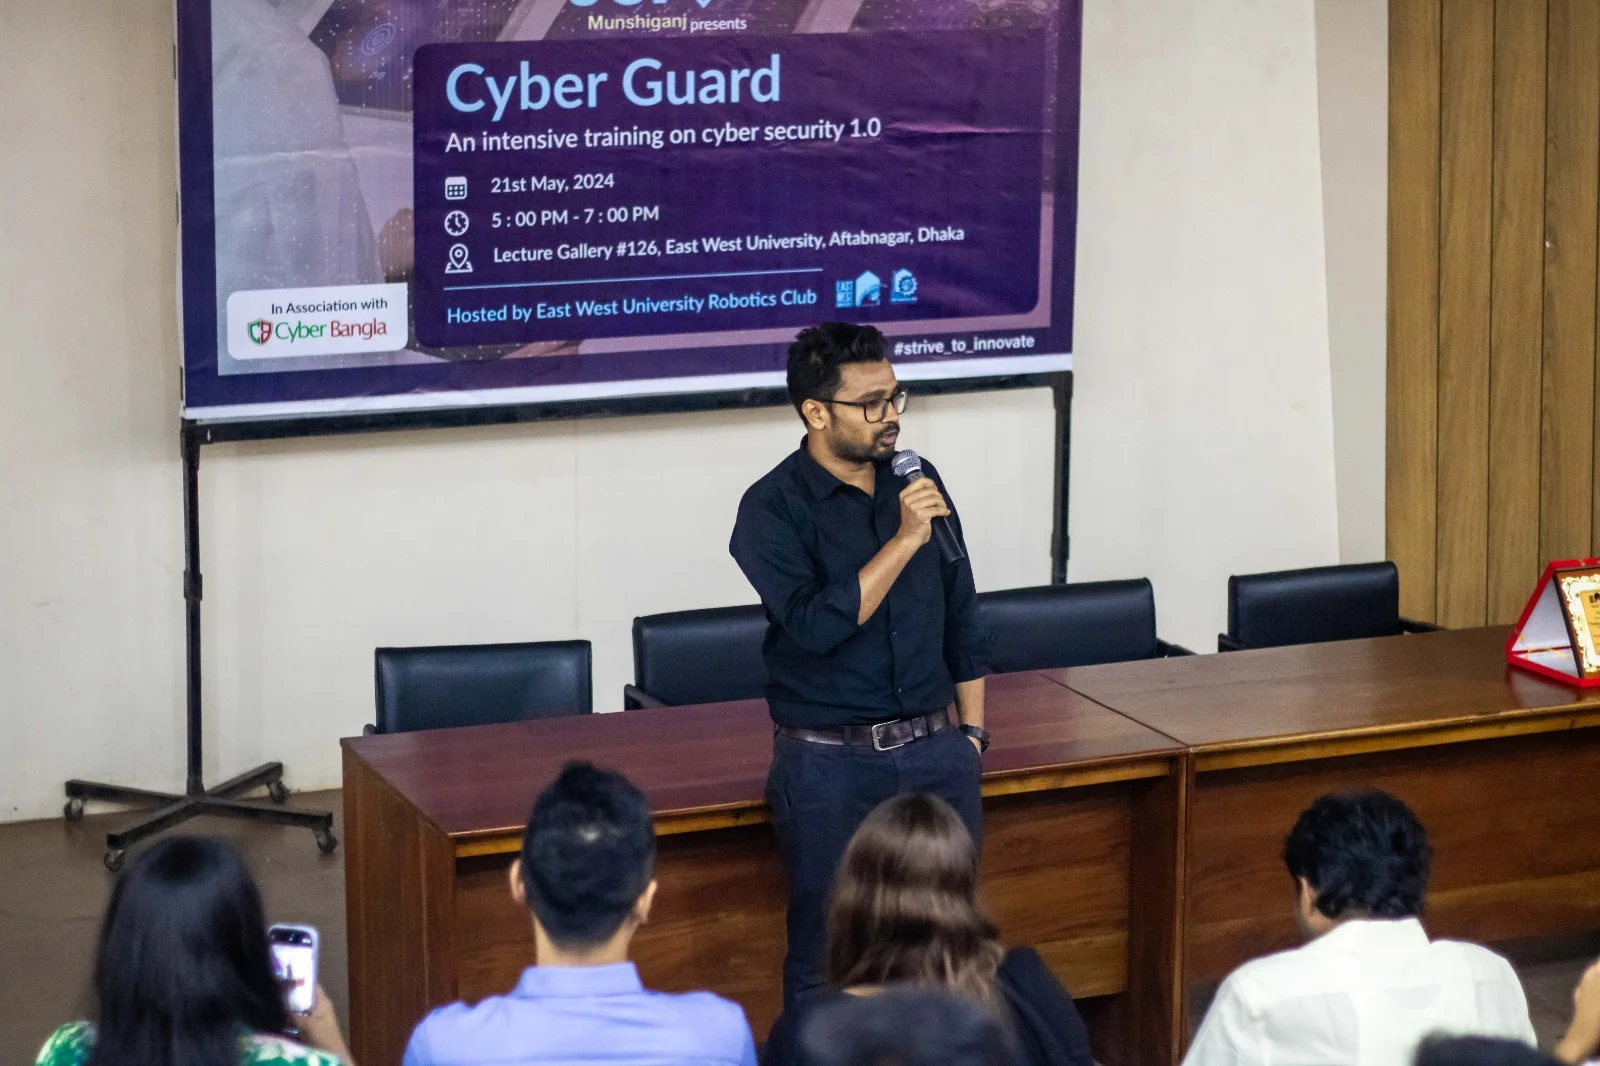
Practical cybersecurity workshops, seminars, and guided learning for teams and student communities. Sessions connect security concepts to hands-on exercises in authorized environments.
Explore this serviceTurn curiosity into real problem-solving experience.
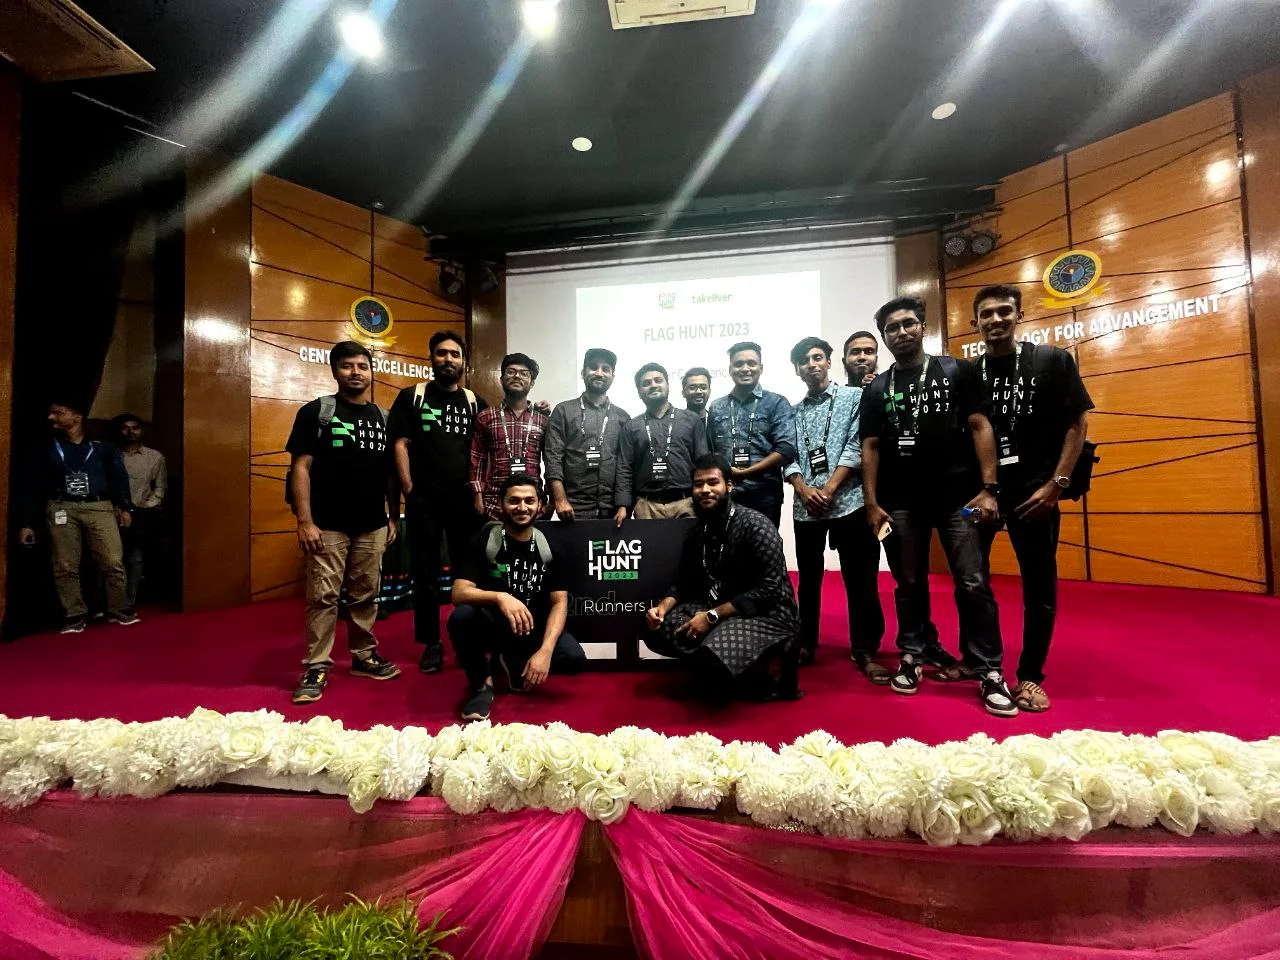
Capture The Flag collaboration for cybersecurity communities and institutions. We bring experience across web security, forensics, cryptography, reverse engineering, and binary exploitation.
Explore this serviceFrom the Black Onion archive

How we work
Good security work is a conversation. We build the scope together, follow the evidence, and leave you with practical next steps.
Listen
01 / 05
Tell us what you’re building, the decisions ahead, and what keeps you up at night. We start by understanding your environment.
Scope
02 / 05
Define the assets, objectives, authorization, and rules of engagement together. A useful assessment begins with a clear plan.
Test
03 / 05
Manual investigation, targeted tools, and an adversary’s perspective. We look at how individual weaknesses connect.
Explain
04 / 05
Reproducible evidence, business context, and practical remediation guidance. We work through the findings with your team.
Improve
05 / 05
Prioritize the fixes, share what we learned, and agree on follow-up testing. Leave your team better informed for the next decision.
Ways to begin
A few illustrative engagement packages to help you explore the possibilities. Final scope, availability, and pricing are agreed with our team.
A focused starting point for teams preparing a web application release.
per application
$1,200
View packageUnderstand what your public footprint reveals before deciding where to invest.
per domain group
$650
View packageConnect security knowledge to practical decisions in a guided team workshop.
per workshop
$900
View packageIllustrative demo prices. No payment is taken on this site. Compare engagements

Founder & Team Lead
Digital forensics

Team Advisor
Cybersecurity engineering

Co-Founder
Penetration testing

Red Team Lead
Offensive security

Web Penetration Tester
Application security

Web Penetration Tester
Application security
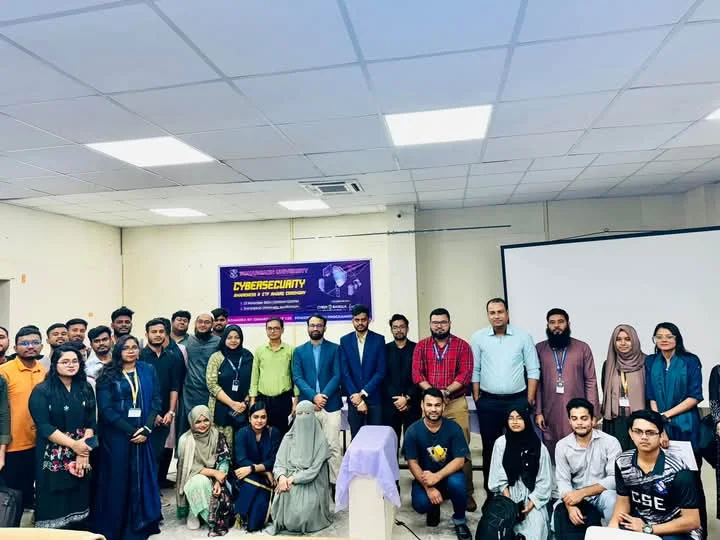
Communities and teams connected by curiosity. We learn together, exchange ideas, and make space for the next collaboration.
University of South Asia
Cybersecurity community
Community collaborator
Our community
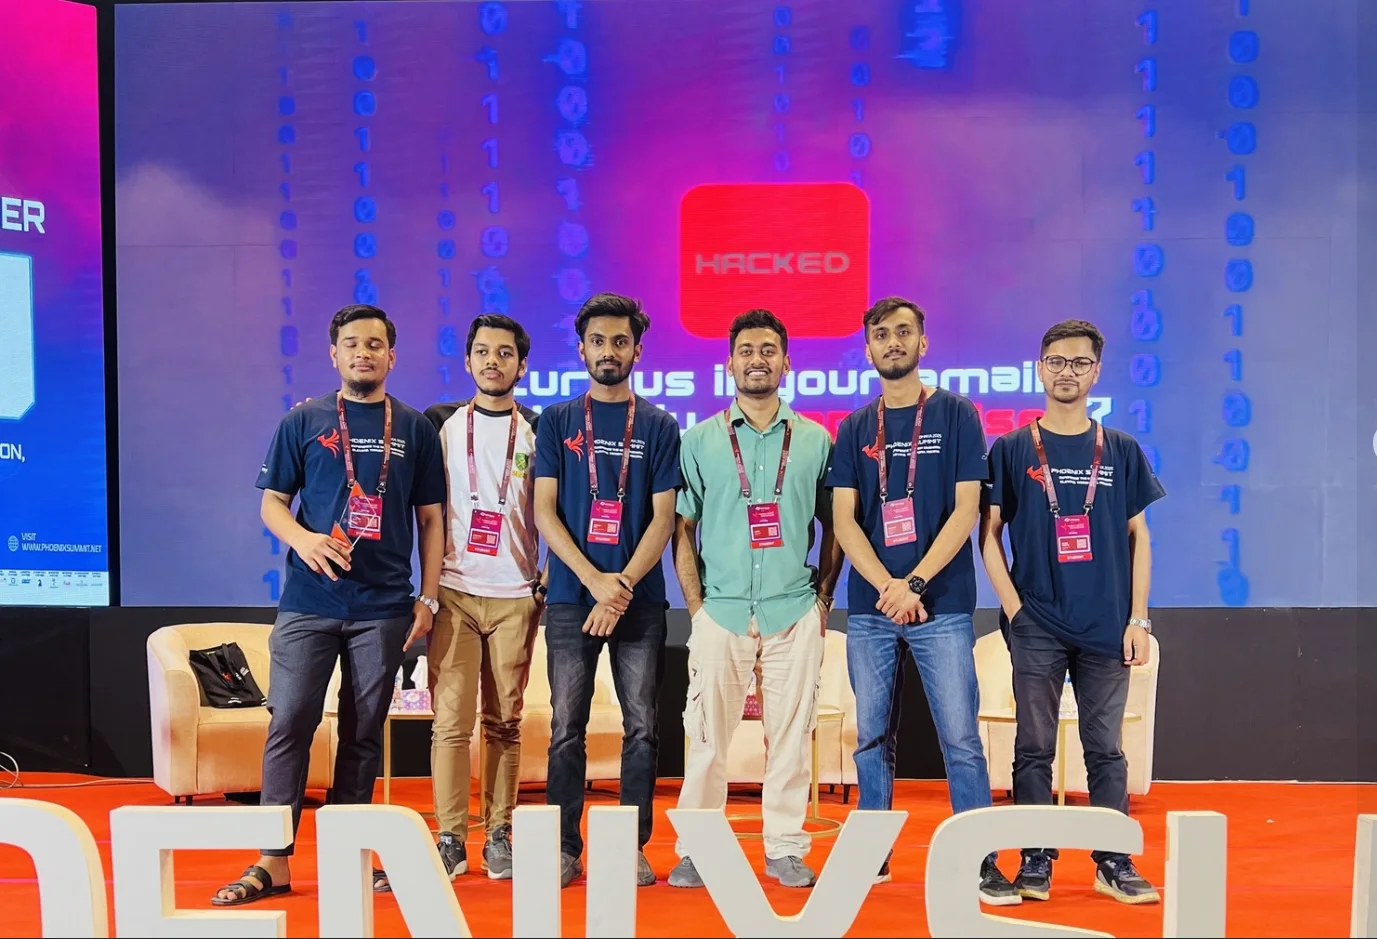
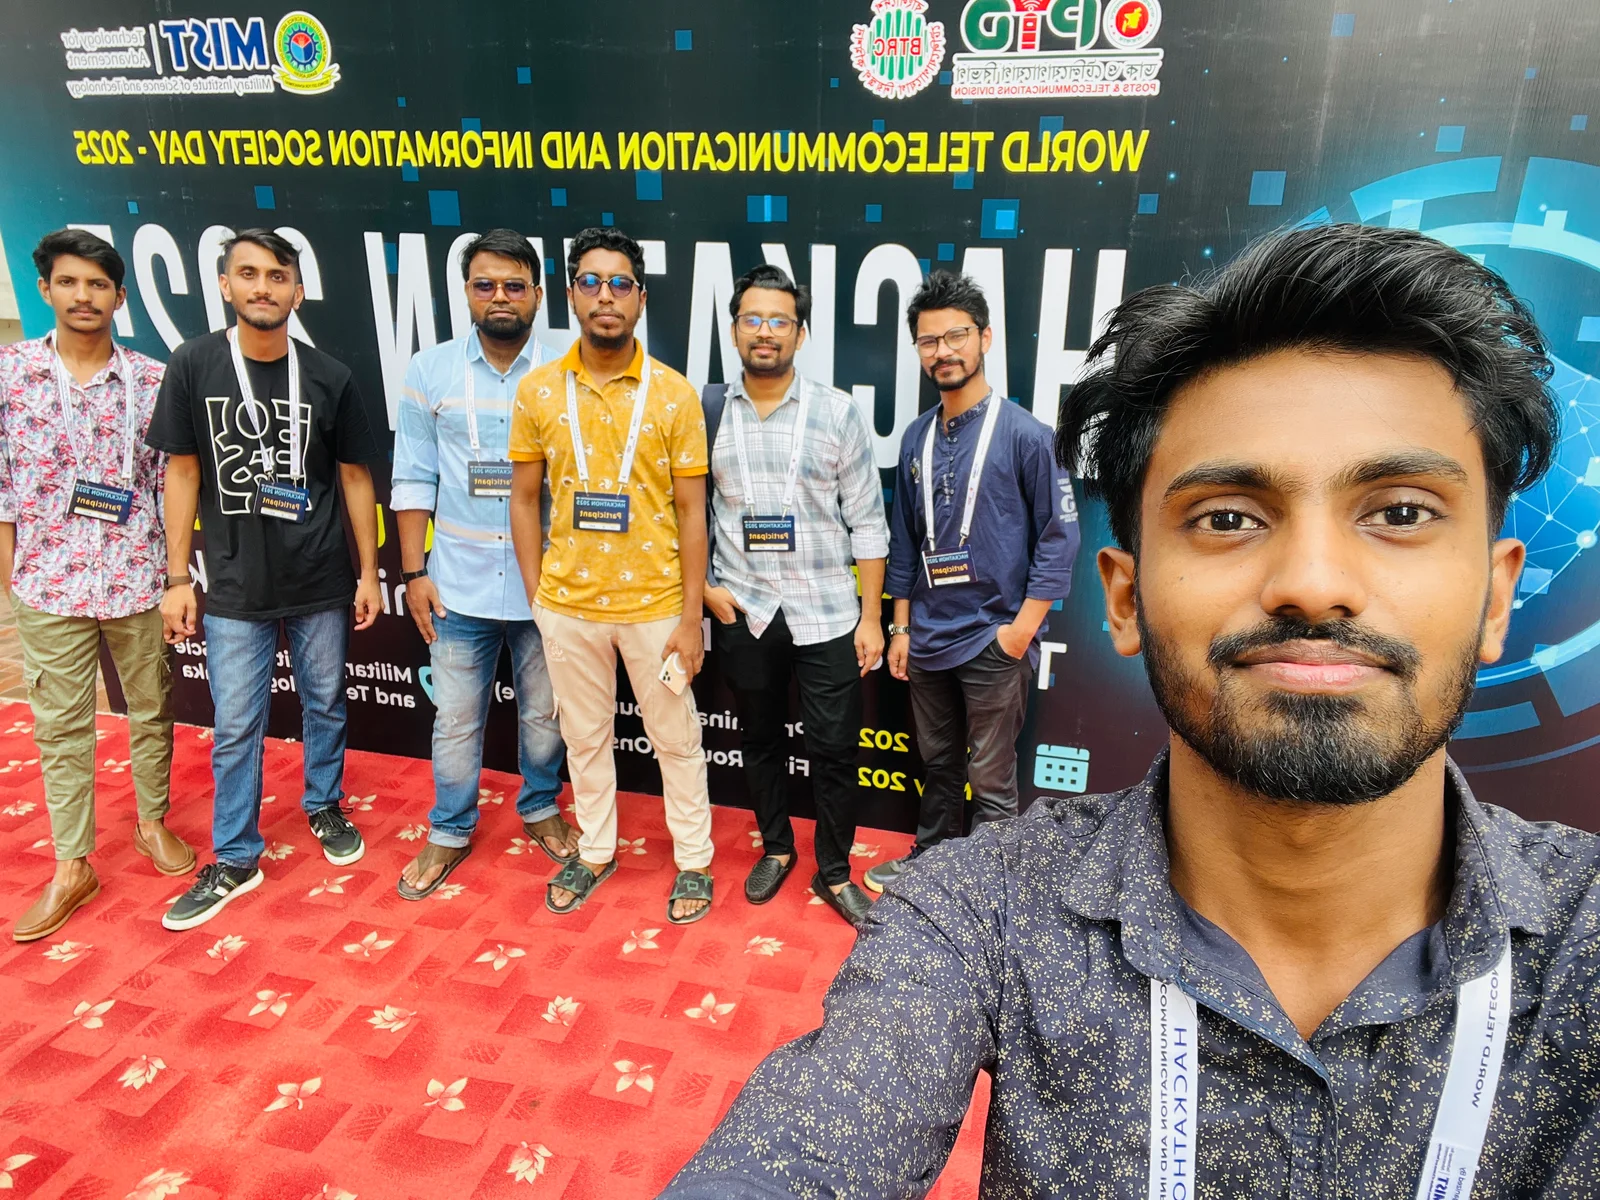
Researchers, builders, students, and the people who keep asking why. We come together through workshops, security events, and Capture The Flag competitions.
On the scoreboard
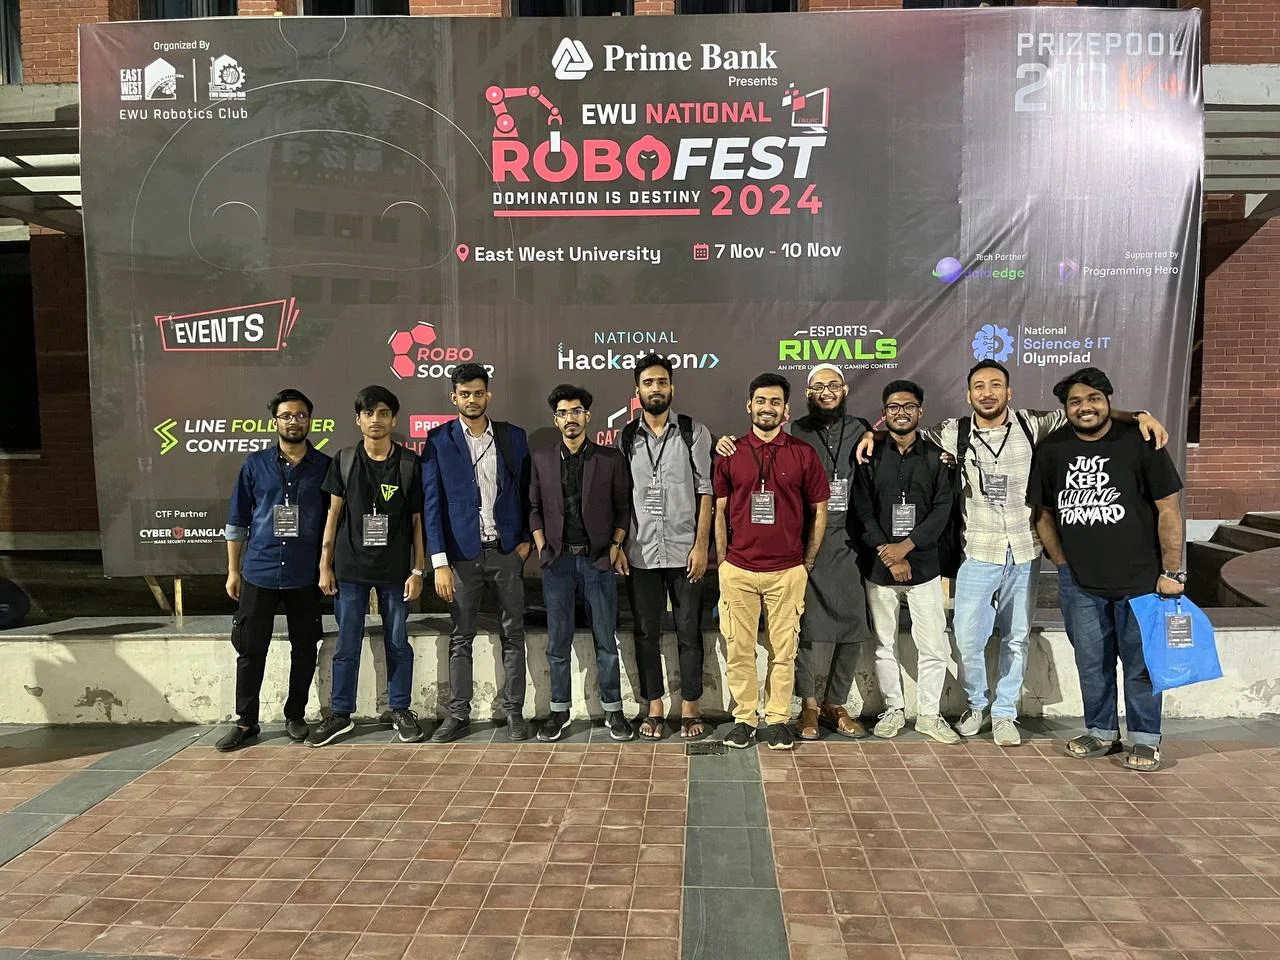
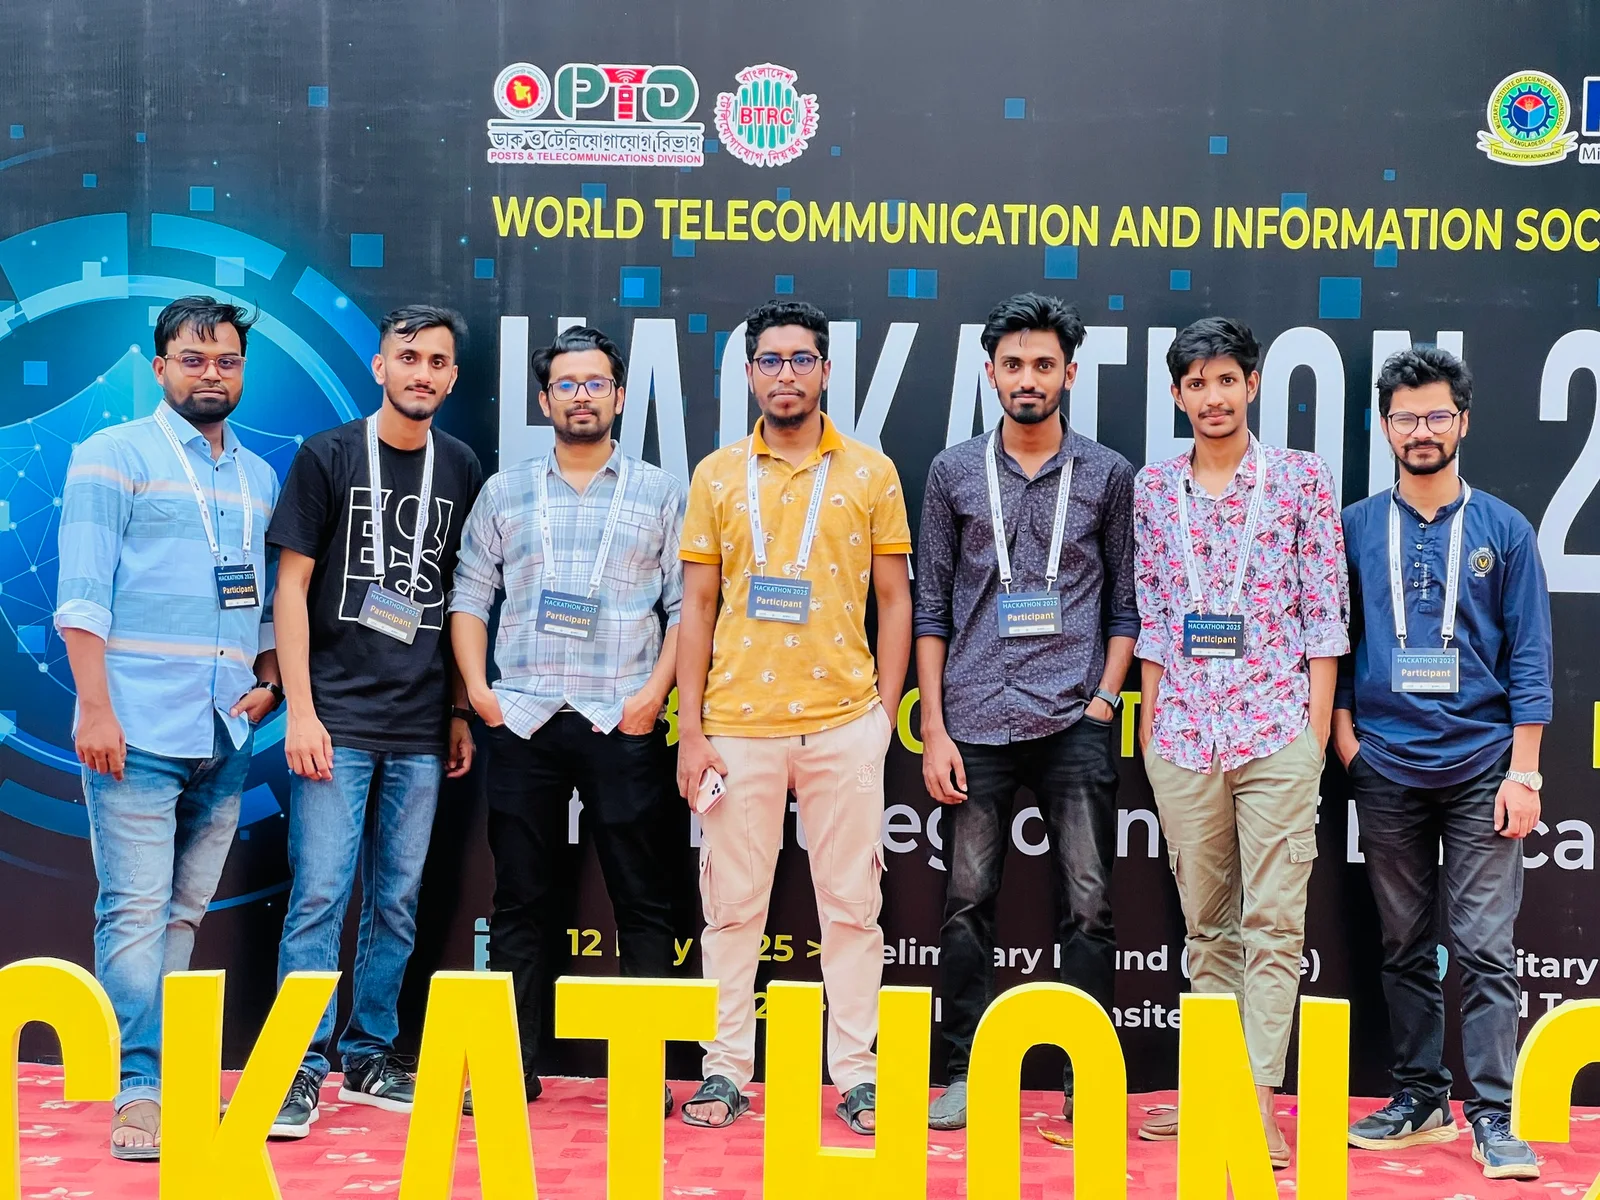
A few results from our competition archive. Every challenge is another reason to research, test an idea, and learn from each other.
2026 / Competition archive
2025 / Competition archive
2025 / Competition archive
2025 / Competition archive
2025 / Competition archive
2025 / Competition archive
2025 / Competition archive
Learn with Black Onion
Sessions shaped around your team’s experience and goals. Controlled labs, guided exercises, and room to ask the questions that matter.
Useful knowledge, shared
The assessment guide
A practical scope and authorization checklist for engineering teams.
Name the decision the assessment should support: a release, an acquisition, or a remediation milestone. Identify the business workflows and data that matter most.
List assets you own or are authorized to test, environments, user roles, and explicit exclusions. Obtain written permission for third-party systems before including them.
Agree on evidence handling, escalation contacts, reporting expectations, and the retest scope. Assign an owner to triage findings and coordinate fixes.
Playbook
A discussion-based rehearsal for decisions, ownership, and escalation.
Read in the resource librarySample case study
An illustrative application assessment, from scope to retest.
Read in the resource libraryGood questions
A little clarity goes a long way. If there’s something else on your mind, get in touch.
Our focus includes web application and API penetration testing, network security assessments, and red teaming. We agree on the assets, objectives, and testing boundaries with you before an engagement begins.
We start with your goals, the systems involved, and operational constraints. Testing begins only after scope, authorization, rules of engagement, and communication channels have been agreed.
Confidentiality requirements, evidence handling, and any NDA are discussed before work starts. Please do not include credentials, sensitive findings, or customer data in an initial inquiry.
Yes. We work with teams, institutions, and cybersecurity communities on practical workshops, seminars, and CTF collaboration. The content is shaped around the audience and their experience.
Timing depends on scope, complexity, access, and availability. Contact us with a high-level description of your environment so we can discuss an appropriate plan.
An engagement can include prioritized findings, remediation guidance, a technical debrief, and a retest plan. Exact deliverables and follow-up activities are agreed as part of the scope.
Let’s talk
Sign in to send your message, keep track of replies, and use the details already on your account.
Sign in to send a message