Curiosity is
our starting point.

Think like an adversary.

Stronger defense starts with a different perspective.

We look beyond an isolated vulnerability to understand how weaknesses connect. Explicit authorization and clear boundaries guide every investigation.
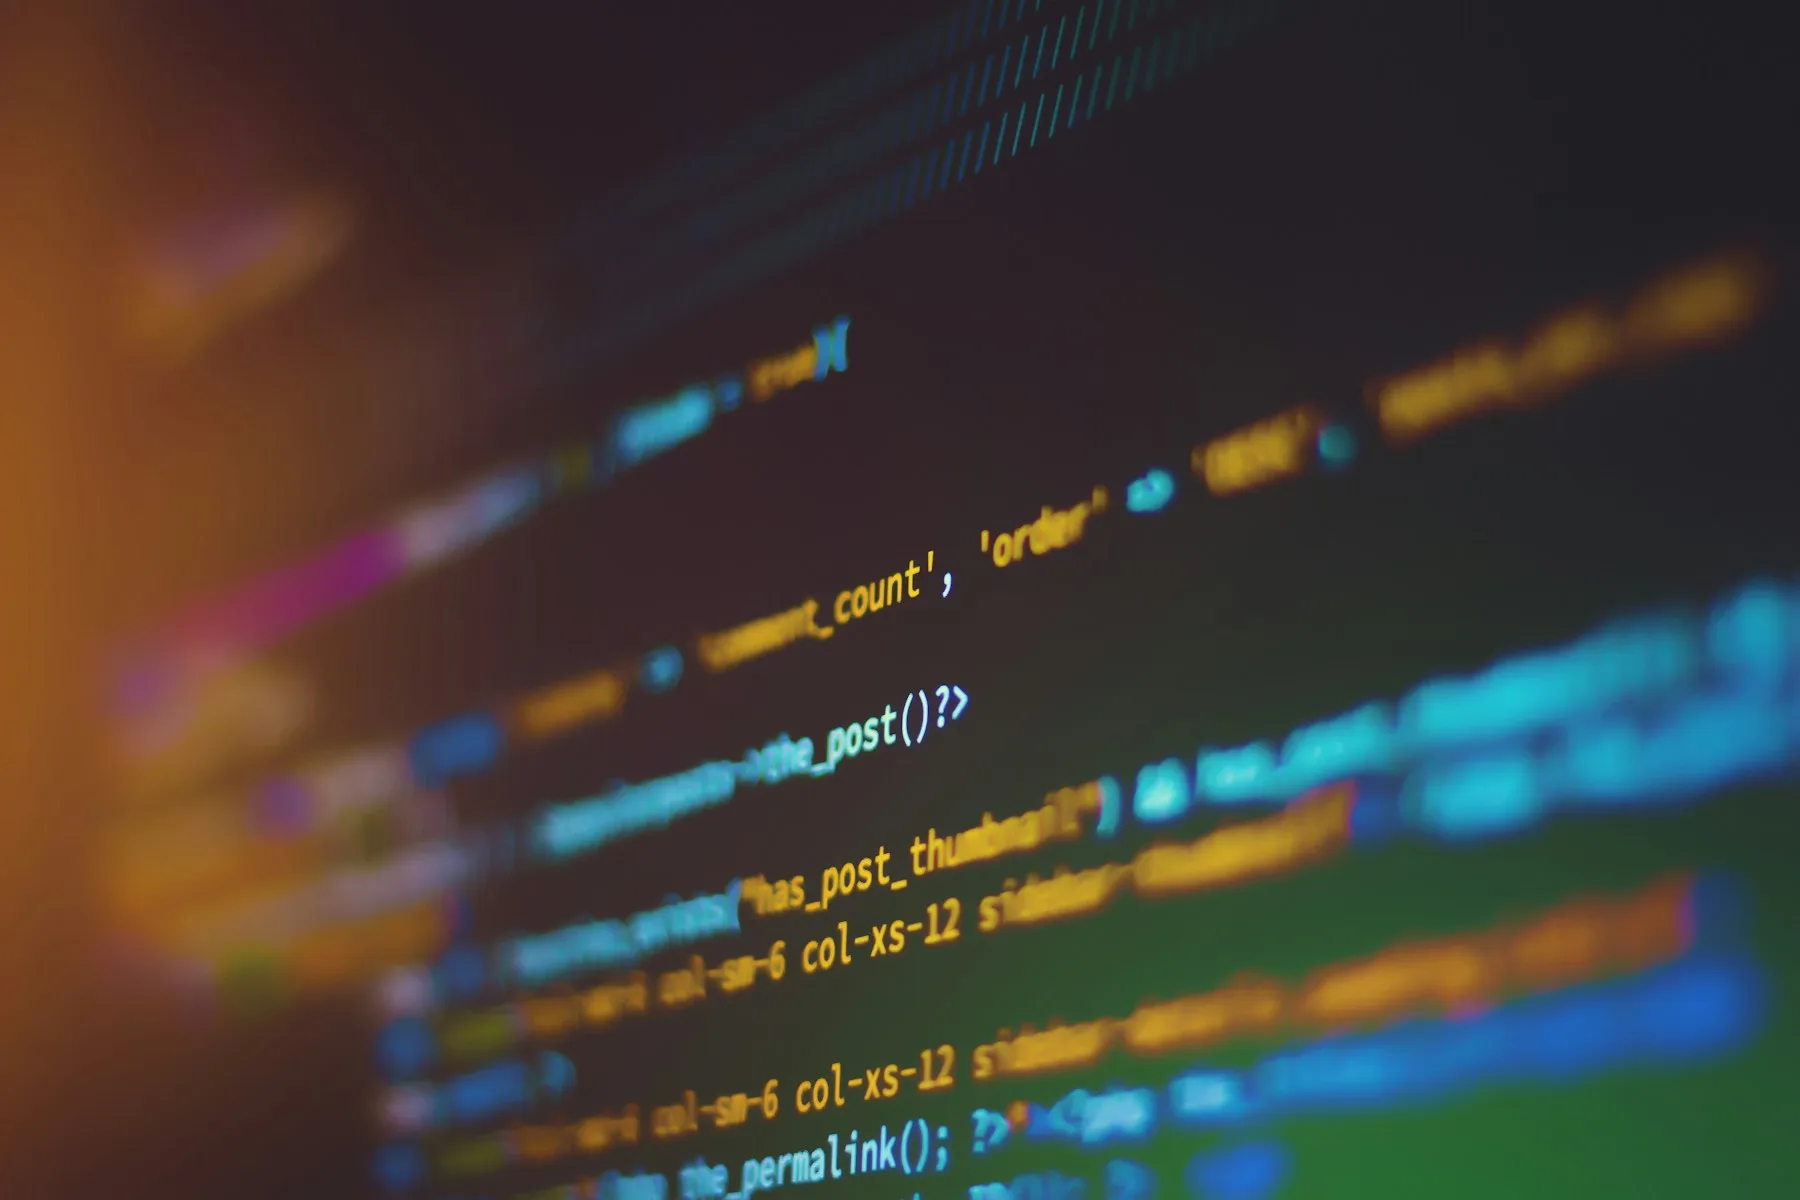
Source code under investigation
  • Manual penetration testing
  • Objective-led red teaming
  • Evidence that engineering teams can reproduce
Explore our offensive work

Stay with the question.

Curiosity is a method, not just a mindset.

Application behavior, binaries, cryptography, and the unexpected paths between them. We investigate how systems work before deciding how they can fail.

Electronic components and circuitry
  • Security research and reverse engineering
  • Public-source threat intelligence
  • Responsible disclosure where applicable
Meet our research approach

Make knowledge travel.

A stronger security community benefits everyone.

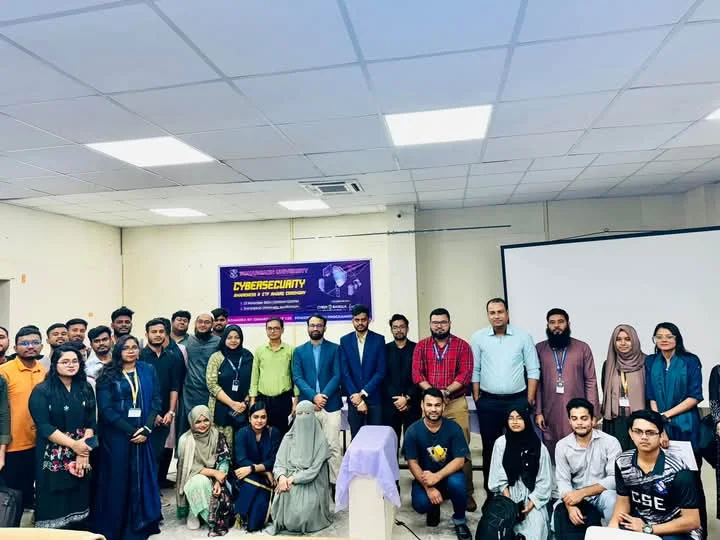
We are a Bangladesh-based collective of ethical hackers, researchers, and builders. Workshops, CTF collaboration, and shared learning connect the work we do.

A workshop from the Black Onion community archive
  • Practical workshops and seminars
  • CTF challenge collaboration
  • Learning alongside teams and institutions
Meet our people
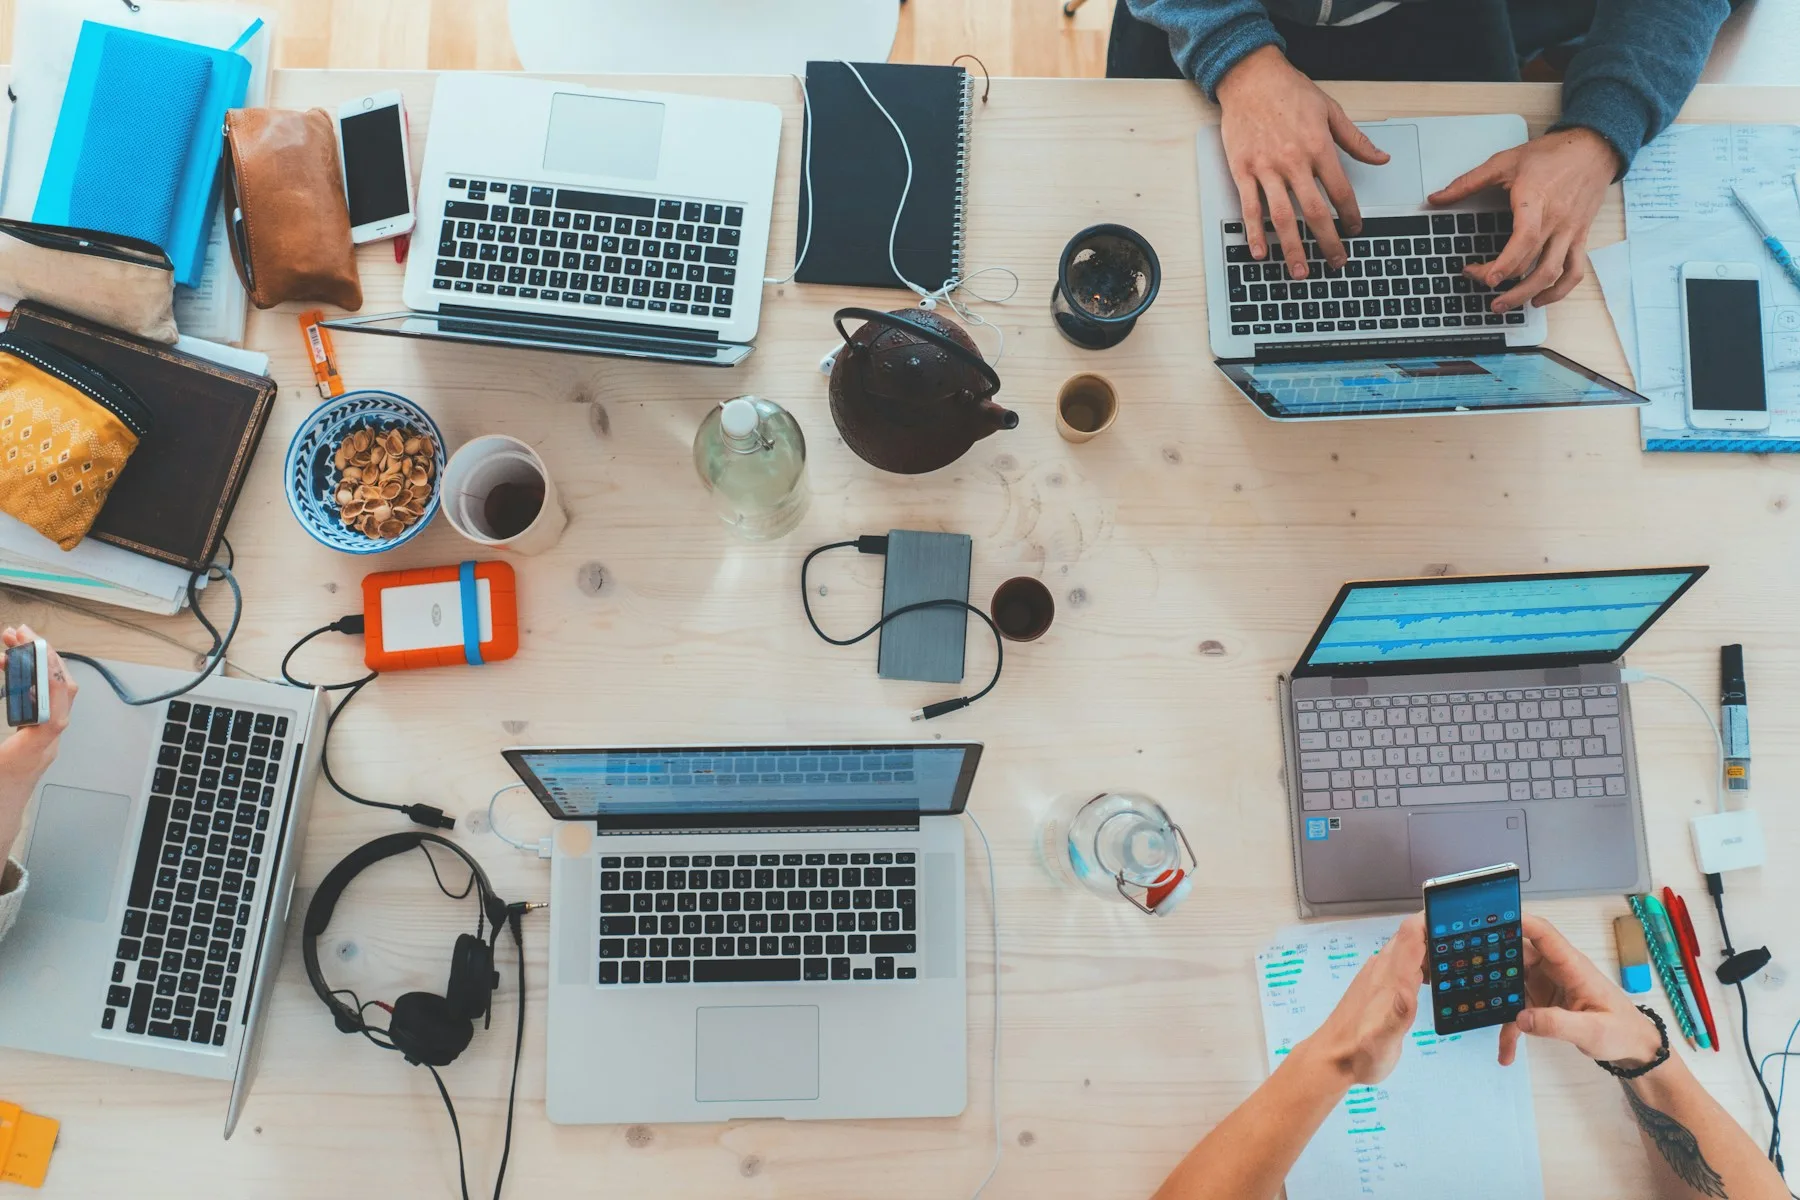
People working together around laptops

The first step

It starts with one conversation.

You do not need a complete security brief to get in touch. Start with what you know. We’ll work through the questions together.

  1. Tell us what matters

    A release, an assessment, a training goal, or a question about your exposure. Share a high-level outline.

  2. Shape the scope together

    We discuss systems, objectives, authorization, and practical constraints. No testing begins without agreed boundaries.

  3. Leave with a useful next step

    The right expertise, a proposed approach, and a clear conversation about what comes next.

Start the conversation

A STRONGER SECURITY POSTURE STARTS HERE

Let's get to the root of it.

Talk to our team